The 35-Watt Roommate (Part 5): Monitoring, or 'Why is the internet constantly asking for my .php files?'
- 1.The 35-Watt Roommate (Part 1): From Memory Hunger to Mini Powerhouse
- 2.The 35-Watt Roommate (Part 2): The Cloud in a Cabinet
- 3.The 35-Watt Roommate (Part 3): Middle-earth and the Digital Infarction
- 4.The 35-Watt Roommate (Part 4): Docker Cleanup and Surgical Data Recovery
- 5.The 35-Watt Roommate (Part 5): Monitoring, or 'Why is the internet constantly asking for my .php files?'
- 6.The 35-Watt Roommate (Part 6): Ads? Never Heard of Them.
- 7.The 35-Watt Roommate (Part 7): Goodbye Fritz!Box, Hello Ubiquiti
- 8.The 35-Watt Roommate (Part 8): Umami Analytics, or How a Password with Special Characters Broke Everything
A Grafana dashboard sounds like an enterprise thing, far too much hassle for a private homelab. I used to think so too.
Terms like Prometheus, Exporter, Loki, and Promtail sound like a lot of overhead and a steep learning curve. But I started playing around with it for fun, and thanks to Docker the whole thing was up and running faster than you can spell “monitoring”. This is how I ended up monitoring my setup and turning away bots at the front door.
What do I actually want to know?
You might remember my setup from the article about Cloudflare Tunnels and Docker Stacks. I want visibility into my Nginx instances, the Proxmox host, the Ubuntu server (including SSH logs), and my Docker containers.
That’s a fair number of endpoints, but there’s a matching exporter for almost all of it:
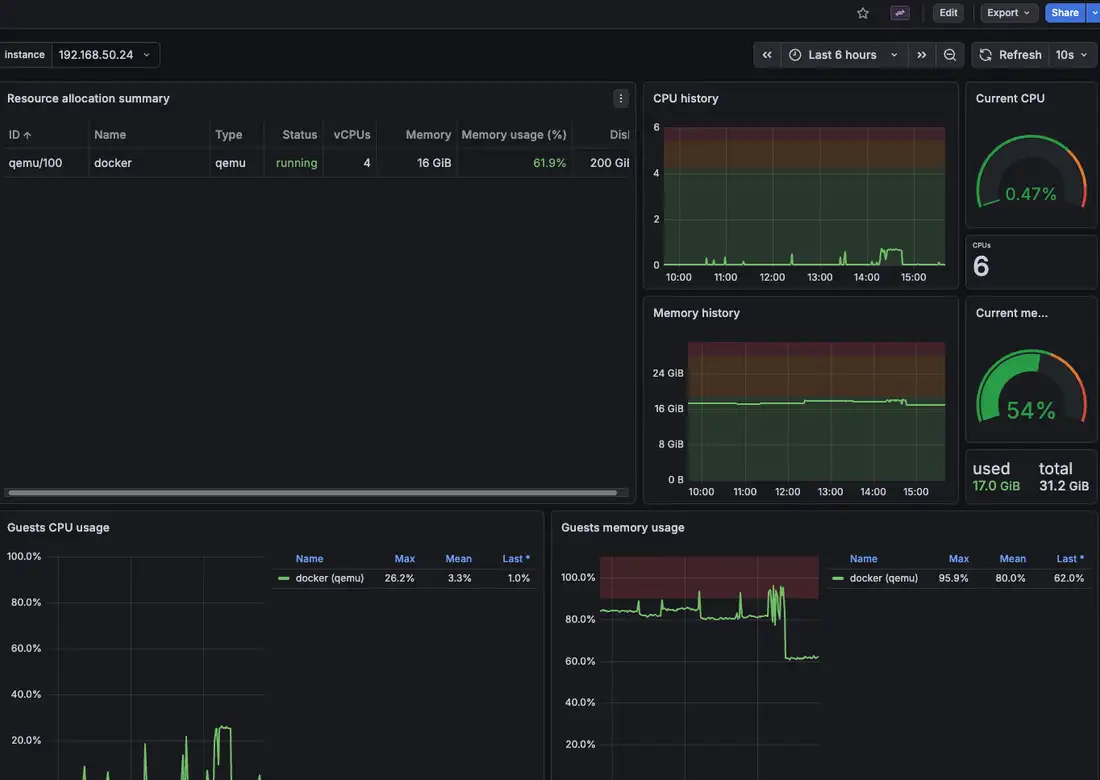
- pve-exporter fetches metrics directly from the Proxmox API.
- node-exporter is the classic for Linux host metrics (CPU, RAM, disk).
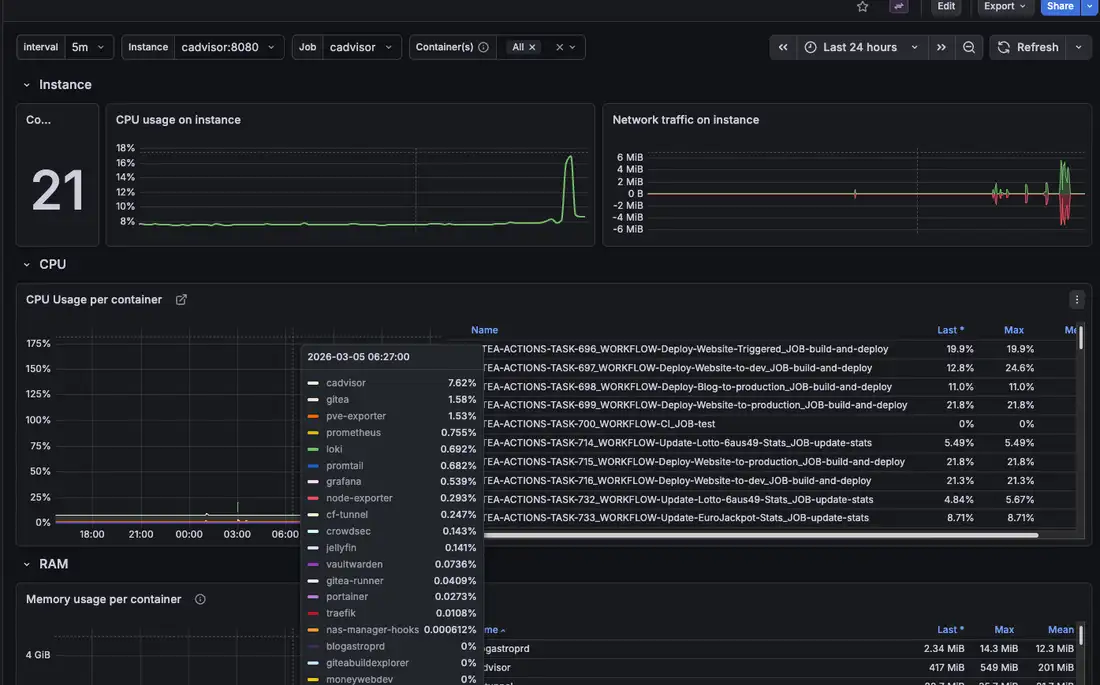
- cAdvisor looks inside Docker containers and cgroups.
- promtail is the log vacuum that ships everything to Loki.
The backend is Loki for logs and Prometheus for time-series metrics. It looks like this:
%3btext-align:center%3b%7d%23mermaid-0 .edgeLabel p%7bbackground-color:rgba(232%2c232%2c232%2c 0.8)%3b%7d%23mermaid-0 .edgeLabel rect%7bopacity:0.5%3bbackground-color:rgba(232%2c232%2c232%2c 0.8)%3bfill:rgba(232%2c232%2c232%2c 0.8)%3b%7d%23mermaid-0 .labelBkg%7bbackground-color:rgba(232%2c 232%2c 232%2c 0.5)%3b%7d%23mermaid-0 .cluster rect%7bfill:%23ffffde%3bstroke:%23aaaa33%3bstroke-width:1px%3b%7d%23mermaid-0 .cluster text%7bfill:%23333%3b%7d%23mermaid-0 .cluster span%7bcolor:%23333%3b%7d%23mermaid-0 .node .collapsed-indicator%7bfill:%23aaaa33%3bstroke:none%3bopacity:0.6%3b%7d%23mermaid-0 .node .collapsed-separator%7bstroke:%23aaaa33%3bstroke-width:0.75px%3b%7d%23mermaid-0 div.mermaidTooltip%7bposition:absolute%3btext-align:center%3bmax-width:200px%3bpadding:2px%3bfont-family:arial%2csans-serif%3bfont-size:12px%3bbackground:hsl(80%2c 100%25%2c 96.2745098039%25)%3bborder:1px solid %23aaaa33%3bborder-radius:2px%3bpointer-events:none%3bz-index:100%3b%7d%23mermaid-0 .flowchartTitleText%7btext-anchor:middle%3bfont-size:18px%3bfill:%23333%3b%7d%23mermaid-0 rect.text%7bfill:none%3bstroke-width:0%3b%7d%23mermaid-0 .icon-shape%2c%23mermaid-0 .image-shape%7bbackground-color:rgba(232%2c232%2c232%2c 0.8)%3btext-align:center%3b%7d%23mermaid-0 .icon-shape p%2c%23mermaid-0 .image-shape p%7bbackground-color:rgba(232%2c232%2c232%2c 0.8)%3bpadding:2px%3b%7d%23mermaid-0 .icon-shape .label rect%2c%23mermaid-0 .image-shape .label rect%7bopacity:0.5%3bbackground-color:rgba(232%2c232%2c232%2c 0.8)%3bfill:rgba(232%2c232%2c232%2c 0.8)%3b%7d%23mermaid-0 .label-icon%7bdisplay:inline-block%3bheight:1em%3boverflow:visible%3bvertical-align:-0.125em%3b%7d%23mermaid-0 .node .label-icon path%7bfill:currentColor%3bstroke:revert%3bstroke-width:revert%3b%7d%23mermaid-0 .node .neo-node%7bstroke:%239370DB%3b%7d%23mermaid-0 %5bdata-look='neo'%5d.node rect%2c%23mermaid-0 %5bdata-look='neo'%5d.cluster rect%2c%23mermaid-0 %5bdata-look='neo'%5d.node polygon%7bstroke:%239370DB%3bfilter:drop-shadow(1px 2px 2px rgba(185%2c 185%2c 185%2c 1))%3b%7d%23mermaid-0 %5bdata-look='neo'%5d.swimlane.cluster rect%7bfilter:none%3b%7d%23mermaid-0 %5bdata-look='neo'%5d.node path%7bstroke:%239370DB%3bstroke-width:1px%3b%7d%23mermaid-0 %5bdata-look='neo'%5d.node .outer-path%7bfilter:drop-shadow(1px 2px 2px rgba(185%2c 185%2c 185%2c 1))%3b%7d%23mermaid-0 %5bdata-look='neo'%5d.node .neo-line path%7bstroke:%239370DB%3bfilter:none%3b%7d%23mermaid-0 %5bdata-look='neo'%5d.node circle%7bstroke:%239370DB%3bfilter:drop-shadow(1px 2px 2px rgba(185%2c 185%2c 185%2c 1))%3b%7d%23mermaid-0 %5bdata-look='neo'%5d.node circle .state-start%7bfill:black%3b%7d%23mermaid-0 %5bdata-look='neo'%5d.icon-shape .icon%7bfill:%239370DB%3bfilter:drop-shadow(1px 2px 2px rgba(185%2c 185%2c 185%2c 1))%3b%7d%23mermaid-0 %5bdata-look='neo'%5d.icon-shape .icon-neo path%7bstroke:%239370DB%3bfilter:drop-shadow(1px 2px 2px rgba(185%2c 185%2c 185%2c 1))%3b%7d%23mermaid-0 :root%7b--mermaid-font-family:arial%2csans-serif%3b%7d%23mermaid-0 .grafana%26gt%3b*%7bfill:rgb(244%2c 122%2c 32)!important%3bstroke:rgb(255%2c 255%2c 255)!important%3bstroke-width:2px!important%3bcolor:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .grafana span%7bfill:rgb(244%2c 122%2c 32)!important%3bstroke:rgb(255%2c 255%2c 255)!important%3bstroke-width:2px!important%3bcolor:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .grafana tspan%7bfill:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .prometheus%26gt%3b*%7bfill:rgb(230%2c 82%2c 44)!important%3bstroke:rgb(255%2c 255%2c 255)!important%3bstroke-width:2px!important%3bcolor:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .prometheus span%7bfill:rgb(230%2c 82%2c 44)!important%3bstroke:rgb(255%2c 255%2c 255)!important%3bstroke-width:2px!important%3bcolor:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .prometheus tspan%7bfill:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .loki%26gt%3b*%7bfill:rgb(0%2c 0%2c 0)!important%3bstroke:rgb(255%2c 255%2c 255)!important%3bstroke-width:2px!important%3bcolor:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .loki span%7bfill:rgb(0%2c 0%2c 0)!important%3bstroke:rgb(255%2c 255%2c 255)!important%3bstroke-width:2px!important%3bcolor:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .loki tspan%7bfill:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .exporter%26gt%3b*%7bfill:rgb(0%2c 163%2c 204)!important%3bstroke:rgb(255%2c 255%2c 255)!important%3bstroke-width:2px!important%3bcolor:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .exporter span%7bfill:rgb(0%2c 163%2c 204)!important%3bstroke:rgb(255%2c 255%2c 255)!important%3bstroke-width:2px!important%3bcolor:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .exporter tspan%7bfill:rgb(255%2c 255%2c 255)!important%3b%7d%23mermaid-0 .source%26gt%3b*%7bfill:rgb(68%2c 68%2c 68)!important%3bstroke:rgb(255%2c 255%2c 255)!important%3bstroke-width:1px!important%3bcolor:rgb(255%2c 255%2c 255)!important%3bstroke-dasharray:5%2c5!important%3b%7d%23mermaid-0 .source span%7bfill:rgb(68%2c 68%2c 68)!important%3bstroke:rgb(255%2c 255%2c 255)!important%3bstroke-width:1px!important%3bcolor:rgb(255%2c 255%2c 255)!important%3bstroke-dasharray:5%2c5!important%3b%7d%23mermaid-0 .source tspan%7bfill:rgb(255%2c 255%2c 255)!important%3b%7d%3c/style%3e%3cg%3e%3cmarker id='mermaid-0_flowchart-v2-pointEnd' class='marker flowchart-v2' viewBox='0 0 10 10' refX='5' refY='5' markerUnits='userSpaceOnUse' markerWidth='8' markerHeight='8' orient='auto'%3e%3cpath d='M 0 0 L 10 5 L 0 10 z' class='arrowMarkerPath' style='stroke-width: 1%3b stroke-dasharray: 1%2c 0%3b'/%3e%3c/marker%3e%3cmarker id='mermaid-0_flowchart-v2-pointStart' class='marker flowchart-v2' viewBox='0 0 10 10' refX='4.5' refY='5' markerUnits='userSpaceOnUse' markerWidth='8' markerHeight='8' orient='auto'%3e%3cpath d='M 0 5 L 10 10 L 10 0 z' class='arrowMarkerPath' style='stroke-width: 1%3b stroke-dasharray: 1%2c 0%3b'/%3e%3c/marker%3e%3cmarker id='mermaid-0_flowchart-v2-pointEnd-margin' class='marker flowchart-v2' viewBox='0 0 11.5 14' refX='11.5' refY='7' markerUnits='userSpaceOnUse' markerWidth='10.5' markerHeight='14' orient='auto'%3e%3cpath d='M 0 0 L 11.5 7 L 0 14 z' class='arrowMarkerPath' style='stroke-width: 0%3b stroke-dasharray: 1%2c 0%3b'/%3e%3c/marker%3e%3cmarker id='mermaid-0_flowchart-v2-pointStart-margin' class='marker flowchart-v2' viewBox='0 0 11.5 14' refX='1' refY='7' markerUnits='userSpaceOnUse' markerWidth='11.5' markerHeight='14' orient='auto'%3e%3cpolygon points='0%2c7 11.5%2c14 11.5%2c0' class='arrowMarkerPath' style='stroke-width: 0%3b stroke-dasharray: 1%2c 0%3b'/%3e%3c/marker%3e%3cmarker id='mermaid-0_flowchart-v2-circleEnd' class='marker flowchart-v2' viewBox='0 0 10 10' refX='11' refY='5' markerUnits='userSpaceOnUse' markerWidth='11' markerHeight='11' orient='auto'%3e%3ccircle cx='5' cy='5' r='5' class='arrowMarkerPath' style='stroke-width: 1%3b stroke-dasharray: 1%2c 0%3b'/%3e%3c/marker%3e%3cmarker id='mermaid-0_flowchart-v2-circleStart' class='marker flowchart-v2' viewBox='0 0 10 10' refX='-1' refY='5' markerUnits='userSpaceOnUse' markerWidth='11' markerHeight='11' orient='auto'%3e%3ccircle cx='5' cy='5' r='5' class='arrowMarkerPath' style='stroke-width: 1%3b stroke-dasharray: 1%2c 0%3b'/%3e%3c/marker%3e%3cmarker id='mermaid-0_flowchart-v2-circleEnd-margin' class='marker flowchart-v2' viewBox='0 0 10 10' refY='5' refX='12.25' markerUnits='userSpaceOnUse' markerWidth='14' markerHeight='14' orient='auto'%3e%3ccircle cx='5' cy='5' r='5' class='arrowMarkerPath' style='stroke-width: 0%3b stroke-dasharray: 1%2c 0%3b'/%3e%3c/marker%3e%3cmarker id='mermaid-0_flowchart-v2-circleStart-margin' class='marker flowchart-v2' viewBox='0 0 10 10' refX='-2' refY='5' markerUnits='userSpaceOnUse' markerWidth='14' markerHeight='14' orient='auto'%3e%3ccircle cx='5' cy='5' r='5' class='arrowMarkerPath' style='stroke-width: 0%3b stroke-dasharray: 1%2c 0%3b'/%3e%3c/marker%3e%3cmarker id='mermaid-0_flowchart-v2-crossEnd' class='marker cross flowchart-v2' viewBox='0 0 11 11' refX='12' refY='5.2' markerUnits='userSpaceOnUse' markerWidth='11' markerHeight='11' orient='auto'%3e%3cpath d='M 1%2c1 l 9%2c9 M 10%2c1 l -9%2c9' class='arrowMarkerPath' style='stroke-width: 2%3b stroke-dasharray: 1%2c 0%3b'/%3e%3c/marker%3e%3cmarker id='mermaid-0_flowchart-v2-crossStart' class='marker cross flowchart-v2' viewBox='0 0 11 11' refX='-1' refY='5.2' markerUnits='userSpaceOnUse' markerWidth='11' markerHeight='11' orient='auto'%3e%3cpath d='M 1%2c1 l 9%2c9 M 10%2c1 l -9%2c9' class='arrowMarkerPath' style='stroke-width: 2%3b stroke-dasharray: 1%2c 0%3b'/%3e%3c/marker%3e%3cmarker id='mermaid-0_flowchart-v2-crossEnd-margin' class='marker cross flowchart-v2' viewBox='0 0 15 15' refX='17.7' refY='7.5' markerUnits='userSpaceOnUse' markerWidth='12' markerHeight='12' orient='auto'%3e%3cpath d='M 1%2c1 L 14%2c14 M 1%2c14 L 14%2c1' class='arrowMarkerPath' style='stroke-width: 2.5%3b'/%3e%3c/marker%3e%3cmarker id='mermaid-0_flowchart-v2-crossStart-margin' class='marker cross flowchart-v2' viewBox='0 0 15 15' refX='-3.5' refY='7.5' markerUnits='userSpaceOnUse' markerWidth='12' markerHeight='12' orient='auto'%3e%3cpath d='M 1%2c1 L 14%2c14 M 1%2c14 L 14%2c1' class='arrowMarkerPath' style='stroke-width: 2.5%3b stroke-dasharray: 1%2c 0%3b'/%3e%3c/marker%3e%3cg class='root'%3e%3cg class='clusters'%3e%3cg class='cluster' id='mermaid-0-Databases' data-look='classic'%3e%3crect style='' x='277.1875' y='512' width='871.8125' height='189'/%3e%3cg class='cluster-label' transform='translate(636.3828125%2c 512)'%3e%3cforeignObject width='153.421875' height='24'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b'%3e%3cspan class='nodeLabel'%3e%3cp%3e%f0%9f%92%be Storage Databases%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='cluster' id='mermaid-0-Agents' data-look='classic'%3e%3crect style='' x='637.1875' y='20' width='214.046875' height='472'/%3e%3cg class='cluster-label' transform='translate(667.5078125%2c 20)'%3e%3cforeignObject width='153.40625' height='24'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b'%3e%3cspan class='nodeLabel'%3e%3cp%3e%f0%9f%a4%96 Agents %26amp%3b Exporters%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='cluster' id='mermaid-0-DataSources' data-look='classic'%3e%3crect style='' x='277.1875' y='8' width='310' height='484'/%3e%3cg class='cluster-label' transform='translate(373.78125%2c 8)'%3e%3cforeignObject width='116.8125' height='24'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b'%3e%3cspan class='nodeLabel'%3e%3cp%3e%f0%9f%94%8d Data Sources%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3c/g%3e%3cg class='edgePaths'%3e%3cpath d='M562.188%2c82L566.354%2c82C570.521%2c82%2c578.854%2c82%2c587.188%2c82C595.521%2c82%2c603.854%2c82%2c612.188%2c82C620.521%2c82%2c628.854%2c82%2c640.301%2c82C651.747%2c82%2c666.307%2c82%2c673.587%2c82L680.867%2c82' id='mermaid-0-L_LogFiles_Promtail_0' class='edge-thickness-normal edge-pattern-dotted edge-thickness-normal edge-pattern-solid flowchart-link' style='%3b' data-edge='true' data-et='edge' data-id='L_LogFiles_Promtail_0' data-points='W3sieCI6NTYyLjE4NzUsInkiOjgyfSx7IngiOjU4Ny4xODc1LCJ5Ijo4Mn0seyJ4Ijo2MTIuMTg3NSwieSI6ODJ9LHsieCI6NjM3LjE4NzUsInkiOjgyfSx7IngiOjY4NC44NjcxODc1LCJ5Ijo4Mn1d' data-look='classic' marker-end='url(%23mermaid-0_flowchart-v2-pointEnd)'/%3e%3cpath d='M803.555%2c82L811.501%2c82C819.448%2c82%2c835.341%2c82%2c847.454%2c164.167C859.568%2c246.333%2c867.901%2c410.667%2c884.605%2c498.717C901.309%2c586.767%2c926.385%2c598.534%2c938.922%2c604.417L951.46%2c610.301' id='mermaid-0-L_Promtail_Loki_0' class='edge-thickness-normal edge-pattern-solid edge-thickness-normal edge-pattern-solid flowchart-link' style='%3b' data-edge='true' data-et='edge' data-id='L_Promtail_Loki_0' data-points='W3sieCI6ODAzLjU1NDY4NzUsInkiOjgyfSx7IngiOjg1MS4yMzQzNzUsInkiOjgyfSx7IngiOjg3Ni4yMzQzNzUsInkiOjU3NX0seyJ4Ijo5NTUuMDgwNjg4NDc2NTYyNSwieSI6NjEyfV0=' data-look='classic' marker-end='url(%23mermaid-0_flowchart-v2-pointEnd)'/%3e%3cpath d='M560.875%2c198L565.26%2c198C569.646%2c198%2c578.417%2c198%2c586.969%2c198C595.521%2c198%2c603.854%2c198%2c612.188%2c198C620.521%2c198%2c628.854%2c198%2c636.521%2c198C644.188%2c198%2c651.188%2c198%2c654.688%2c198L658.188%2c198' id='mermaid-0-L_HostOS_NodeExporter_0' class='edge-thickness-normal edge-pattern-dotted edge-thickness-normal edge-pattern-solid flowchart-link' style='%3b' data-edge='true' data-et='edge' data-id='L_HostOS_NodeExporter_0' data-points='W3sieCI6NTYwLjg3NSwieSI6MTk4fSx7IngiOjU4Ny4xODc1LCJ5IjoxOTh9LHsieCI6NjEyLjE4NzUsInkiOjE5OH0seyJ4Ijo2MzcuMTg3NSwieSI6MTk4fSx7IngiOjY2Mi4xODc1LCJ5IjoxOTh9XQ==' data-look='classic' marker-end='url(%23mermaid-0_flowchart-v2-pointEnd)'/%3e%3cpath d='M562.188%2c314L566.354%2c314C570.521%2c314%2c578.854%2c314%2c587.188%2c314C595.521%2c314%2c603.854%2c314%2c612.188%2c314C620.521%2c314%2c628.854%2c314%2c640.078%2c314C651.302%2c314%2c665.417%2c314%2c672.474%2c314L679.531%2c314' id='mermaid-0-L_DockerEngine_cAdvisor_0' class='edge-thickness-normal edge-pattern-dotted edge-thickness-normal edge-pattern-solid flowchart-link' style='%3b' data-edge='true' data-et='edge' data-id='L_DockerEngine_cAdvisor_0' data-points='W3sieCI6NTYyLjE4NzUsInkiOjMxNH0seyJ4Ijo1ODcuMTg3NSwieSI6MzE0fSx7IngiOjYxMi4xODc1LCJ5IjozMTR9LHsieCI6NjM3LjE4NzUsInkiOjMxNH0seyJ4Ijo2ODMuNTMxMjUsInkiOjMxNH1d' data-look='classic' marker-end='url(%23mermaid-0_flowchart-v2-pointEnd)'/%3e%3cpath d='M527.094%2c430L537.109%2c430C547.125%2c430%2c567.156%2c430%2c581.339%2c430C595.521%2c430%2c603.854%2c430%2c612.188%2c430C620.521%2c430%2c628.854%2c430%2c637.04%2c430C645.227%2c430%2c653.266%2c430%2c657.285%2c430L661.305%2c430' id='mermaid-0-L_ProxmoxAPI_PVEExporter_0' class='edge-thickness-normal edge-pattern-dotted edge-thickness-normal edge-pattern-solid flowchart-link' style='%3b' data-edge='true' data-et='edge' data-id='L_ProxmoxAPI_PVEExporter_0' data-points='W3sieCI6NTI3LjA5Mzc1LCJ5Ijo0MzB9LHsieCI6NTg3LjE4NzUsInkiOjQzMH0seyJ4Ijo2MTIuMTg3NSwieSI6NDMwfSx7IngiOjYzNy4xODc1LCJ5Ijo0MzB9LHsieCI6NjY1LjMwNDY4NzUsInkiOjQzMH1d' data-look='classic' marker-end='url(%23mermaid-0_flowchart-v2-pointEnd)'/%3e%3cpath d='M562.188%2c554.968L566.354%2c553.973C570.521%2c552.978%2c578.854%2c550.989%2c587.188%2c549.995C595.521%2c549%2c603.854%2c549%2c612.188%2c549C620.521%2c549%2c628.854%2c549%2c649.292%2c495.638C669.729%2c442.275%2c702.27%2c335.551%2c718.541%2c282.188L734.812%2c228.826' id='mermaid-0-L_Prometheus_NodeExporter_0' class='edge-thickness-normal edge-pattern-solid edge-thickness-normal edge-pattern-solid flowchart-link' style='%3b' data-edge='true' data-et='edge' data-id='L_Prometheus_NodeExporter_0' data-points='W3sieCI6NTYyLjE4NzUsInkiOjU1NC45Njc3NDE5MzU0ODM5fSx7IngiOjU4Ny4xODc1LCJ5Ijo1NDl9LHsieCI6NjEyLjE4NzUsInkiOjU0OX0seyJ4Ijo2MzcuMTg3NSwieSI6NTQ5fSx7IngiOjczNS45NzgzNjUzODQ2MTU0LCJ5IjoyMjV9XQ==' data-look='classic' marker-end='url(%23mermaid-0_flowchart-v2-pointEnd)'/%3e%3cpath d='M562.188%2c586L566.354%2c586C570.521%2c586%2c578.854%2c586%2c587.188%2c586C595.521%2c586%2c603.854%2c586%2c612.188%2c586C620.521%2c586%2c628.854%2c586%2c648.843%2c545.787C668.833%2c505.574%2c700.478%2c425.148%2c716.3%2c384.935L732.123%2c344.722' id='mermaid-0-L_Prometheus_cAdvisor_0' class='edge-thickness-normal edge-pattern-solid edge-thickness-normal edge-pattern-solid flowchart-link' style='%3b' data-edge='true' data-et='edge' data-id='L_Prometheus_cAdvisor_0' data-points='W3sieCI6NTYyLjE4NzUsInkiOjU4Nn0seyJ4Ijo1ODcuMTg3NSwieSI6NTg2fSx7IngiOjYxMi4xODc1LCJ5Ijo1ODZ9LHsieCI6NjM3LjE4NzUsInkiOjU4Nn0seyJ4Ijo3MzMuNTg3Mjg3NDU0MDQ0MSwieSI6MzQxfV0=' data-look='classic' marker-end='url(%23mermaid-0_flowchart-v2-pointEnd)'/%3e%3cpath d='M562.188%2c617.032L566.354%2c618.027C570.521%2c619.022%2c578.854%2c621.011%2c587.188%2c622.005C595.521%2c623%2c603.854%2c623%2c612.188%2c623C620.521%2c623%2c628.854%2c623%2c648.039%2c595.916C667.225%2c568.833%2c697.262%2c514.665%2c712.28%2c487.582L727.299%2c460.498' id='mermaid-0-L_Prometheus_PVEExporter_0' class='edge-thickness-normal edge-pattern-solid edge-thickness-normal edge-pattern-solid flowchart-link' style='%3b' data-edge='true' data-et='edge' data-id='L_Prometheus_PVEExporter_0' data-points='W3sieCI6NTYyLjE4NzUsInkiOjYxNy4wMzIyNTgwNjQ1MTYxfSx7IngiOjU4Ny4xODc1LCJ5Ijo2MjN9LHsieCI6NjEyLjE4NzUsInkiOjYyM30seyJ4Ijo2MzcuMTg3NSwieSI6NjIzfSx7IngiOjcyOS4yMzg3NDY3NjE2NTgsInkiOjQ1N31d' data-look='classic' marker-end='url(%23mermaid-0_flowchart-v2-pointEnd)'/%3e%3cpath d='M215.811%2c650L221.874%2c651.667C227.936%2c653.333%2c240.062%2c656.667%2c250.291%2c658.333C260.521%2c660%2c268.854%2c660%2c298.854%2c660C328.854%2c660%2c380.521%2c660%2c432.188%2c660C483.854%2c660%2c535.521%2c660%2c565.521%2c660C595.521%2c660%2c603.854%2c660%2c612.188%2c660C620.521%2c660%2c628.854%2c660%2c650.858%2c660C672.862%2c660%2c708.536%2c660%2c744.211%2c660C779.885%2c660%2c815.56%2c660%2c837.564%2c660C859.568%2c660%2c867.901%2c660%2c875.575%2c659.46C883.25%2c658.92%2c890.265%2c657.84%2c893.773%2c657.299L897.281%2c656.759' id='mermaid-0-L_Grafana_Loki_0' class='edge-thickness-normal edge-pattern-solid edge-thickness-normal edge-pattern-solid flowchart-link' style='%3b' data-edge='true' data-et='edge' data-id='L_Grafana_Loki_0' data-points='W3sieCI6MjE1LjgxMDgxMDgxMDgxMDgsInkiOjY1MH0seyJ4IjoyNTIuMTg3NSwieSI6NjYwfSx7IngiOjI3Ny4xODc1LCJ5Ijo2NjB9LHsieCI6NDMyLjE4NzUsInkiOjY2MH0seyJ4Ijo1ODcuMTg3NSwieSI6NjYwfSx7IngiOjYxMi4xODc1LCJ5Ijo2NjB9LHsieCI6NjM3LjE4NzUsInkiOjY2MH0seyJ4Ijo3NDQuMjEwOTM3NSwieSI6NjYwfSx7IngiOjg1MS4yMzQzNzUsInkiOjY2MH0seyJ4Ijo4NzYuMjM0Mzc1LCJ5Ijo2NjB9LHsieCI6OTAxLjIzNDM3NSwieSI6NjU2LjE1MDU0MTMzMDEyNTR9XQ==' data-look='classic' marker-end='url(%23mermaid-0_flowchart-v2-pointEnd)'/%3e%3cpath d='M215.811%2c596L221.874%2c594.333C227.936%2c592.667%2c240.062%2c589.333%2c250.291%2c587.667C260.521%2c586%2c268.854%2c586%2c276.521%2c586C284.188%2c586%2c291.188%2c586%2c294.688%2c586L298.188%2c586' id='mermaid-0-L_Grafana_Prometheus_0' class='edge-thickness-normal edge-pattern-solid edge-thickness-normal edge-pattern-solid flowchart-link' style='%3b' data-edge='true' data-et='edge' data-id='L_Grafana_Prometheus_0' data-points='W3sieCI6MjE1LjgxMDgxMDgxMDgxMDgsInkiOjU5Nn0seyJ4IjoyNTIuMTg3NSwieSI6NTg2fSx7IngiOjI3Ny4xODc1LCJ5Ijo1ODZ9LHsieCI6MzAyLjE4NzUsInkiOjU4Nn1d' data-look='classic' marker-end='url(%23mermaid-0_flowchart-v2-pointEnd)'/%3e%3c/g%3e%3cg class='edgeLabels'%3e%3cg class='edgeLabel'%3e%3cg class='label' data-id='L_LogFiles_Promtail_0' transform='translate(0%2c 0)'%3e%3cforeignObject width='0' height='0'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' class='labelBkg' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b'%3e%3cspan class='edgeLabel'%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='edgeLabel'%3e%3cg class='label' data-id='L_Promtail_Loki_0' transform='translate(0%2c 0)'%3e%3cforeignObject width='0' height='0'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' class='labelBkg' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b'%3e%3cspan class='edgeLabel'%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='edgeLabel'%3e%3cg class='label' data-id='L_HostOS_NodeExporter_0' transform='translate(0%2c 0)'%3e%3cforeignObject width='0' height='0'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' class='labelBkg' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b'%3e%3cspan class='edgeLabel'%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='edgeLabel'%3e%3cg class='label' data-id='L_DockerEngine_cAdvisor_0' transform='translate(0%2c 0)'%3e%3cforeignObject width='0' height='0'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' class='labelBkg' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b'%3e%3cspan class='edgeLabel'%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='edgeLabel'%3e%3cg class='label' data-id='L_ProxmoxAPI_PVEExporter_0' transform='translate(0%2c 0)'%3e%3cforeignObject width='0' height='0'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' class='labelBkg' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b'%3e%3cspan class='edgeLabel'%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='edgeLabel'%3e%3cg class='label' data-id='L_Prometheus_NodeExporter_0' transform='translate(0%2c 0)'%3e%3cforeignObject width='0' height='0'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' class='labelBkg' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b'%3e%3cspan class='edgeLabel'%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='edgeLabel'%3e%3cg class='label' data-id='L_Prometheus_cAdvisor_0' transform='translate(0%2c 0)'%3e%3cforeignObject width='0' height='0'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' class='labelBkg' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b'%3e%3cspan class='edgeLabel'%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='edgeLabel'%3e%3cg class='label' data-id='L_Prometheus_PVEExporter_0' transform='translate(0%2c 0)'%3e%3cforeignObject width='0' height='0'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' class='labelBkg' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b'%3e%3cspan class='edgeLabel'%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='edgeLabel'%3e%3cg class='label' data-id='L_Grafana_Loki_0' transform='translate(0%2c 0)'%3e%3cforeignObject width='0' height='0'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' class='labelBkg' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b'%3e%3cspan class='edgeLabel'%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='edgeLabel'%3e%3cg class='label' data-id='L_Grafana_Prometheus_0' transform='translate(0%2c 0)'%3e%3cforeignObject width='0' height='0'%3e%3cdiv xmlns='http://www.w3.org/1999/xhtml' class='labelBkg' style='display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b'%3e%3cspan class='edgeLabel'%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3c/g%3e%3cg class='nodes'%3e%3cg class='node default source' id='mermaid-0-flowchart-LogFiles-0' data-look='classic' transform='translate(432.1875%2c 82)'%3e%3crect class='basic label-container' style='fill:%23444 !important%3bstroke:white !important%3bstroke-width:1px !important%3bstroke-dasharray:5 5 !important' x='-130' y='-39' width='260' height='78'/%3e%3cg class='label' style='color:white !important' transform='translate(-100%2c -24)'%3e%3crect/%3e%3cforeignObject width='200' height='48'%3e%3cdiv style='color: rgb(255%2c 255%2c 255) !important%3b display: table%3b white-space: break-spaces%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b width: 200px%3b' xmlns='http://www.w3.org/1999/xhtml'%3e%3cspan style='color:white !important' class='nodeLabel'%3e%3cp%3eLogfiles (Journal%2c Fail2ban%2c Docker Socket)%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='node default source' id='mermaid-0-flowchart-HostOS-1' data-look='classic' transform='translate(432.1875%2c 198)'%3e%3crect class='basic label-container' style='fill:%23444 !important%3bstroke:white !important%3bstroke-width:1px !important%3bstroke-dasharray:5 5 !important' x='-128.6875' y='-27' width='257.375' height='54'/%3e%3cg class='label' style='color:white !important' transform='translate(-98.6875%2c -12)'%3e%3crect/%3e%3cforeignObject width='197.375' height='24'%3e%3cdiv style='color: rgb(255%2c 255%2c 255) !important%3b display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b' xmlns='http://www.w3.org/1999/xhtml'%3e%3cspan style='color:white !important' class='nodeLabel'%3e%3cp%3eHost OS (/proc%2c /sys%2c rootfs)%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='node default source' id='mermaid-0-flowchart-DockerEngine-2' data-look='classic' transform='translate(432.1875%2c 314)'%3e%3crect class='basic label-container' style='fill:%23444 !important%3bstroke:white !important%3bstroke-width:1px !important%3bstroke-dasharray:5 5 !important' x='-130' y='-39' width='260' height='78'/%3e%3cg class='label' style='color:white !important' transform='translate(-100%2c -24)'%3e%3crect/%3e%3cforeignObject width='200' height='48'%3e%3cdiv style='color: rgb(255%2c 255%2c 255) !important%3b display: table%3b white-space: break-spaces%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b width: 200px%3b' xmlns='http://www.w3.org/1999/xhtml'%3e%3cspan style='color:white !important' class='nodeLabel'%3e%3cp%3eDocker Engine (Containers%2c cgroups)%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='node default source' id='mermaid-0-flowchart-ProxmoxAPI-3' data-look='classic' transform='translate(432.1875%2c 430)'%3e%3crect class='basic label-container' style='fill:%23444 !important%3bstroke:white !important%3bstroke-width:1px !important%3bstroke-dasharray:5 5 !important' x='-94.90625' y='-27' width='189.8125' height='54'/%3e%3cg class='label' style='color:white !important' transform='translate(-64.90625%2c -12)'%3e%3crect/%3e%3cforeignObject width='129.8125' height='24'%3e%3cdiv style='color: rgb(255%2c 255%2c 255) !important%3b display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b' xmlns='http://www.w3.org/1999/xhtml'%3e%3cspan style='color:white !important' class='nodeLabel'%3e%3cp%3eProxmox VE (API)%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='node default exporter' id='mermaid-0-flowchart-Promtail-4' data-look='classic' transform='translate(744.2109375%2c 82)'%3e%3crect class='basic label-container' style='fill:%2300a3cc !important%3bstroke:white !important%3bstroke-width:2px !important' x='-59.34375' y='-27' width='118.6875' height='54'/%3e%3cg class='label' style='color:white !important' transform='translate(-29.34375%2c -12)'%3e%3crect/%3e%3cforeignObject width='58.6875' height='24'%3e%3cdiv style='color: rgb(255%2c 255%2c 255) !important%3b display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b' xmlns='http://www.w3.org/1999/xhtml'%3e%3cspan style='color:white !important' class='nodeLabel'%3e%3cp%3ePromtail%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='node default exporter' id='mermaid-0-flowchart-NodeExporter-5' data-look='classic' transform='translate(744.2109375%2c 198)'%3e%3crect class='basic label-container' style='fill:%2300a3cc !important%3bstroke:white !important%3bstroke-width:2px !important' x='-82.0234375' y='-27' width='164.046875' height='54'/%3e%3cg class='label' style='color:white !important' transform='translate(-52.0234375%2c -12)'%3e%3crect/%3e%3cforeignObject width='104.046875' height='24'%3e%3cdiv style='color: rgb(255%2c 255%2c 255) !important%3b display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b' xmlns='http://www.w3.org/1999/xhtml'%3e%3cspan style='color:white !important' class='nodeLabel'%3e%3cp%3eNode-Exporter%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='node default exporter' id='mermaid-0-flowchart-cAdvisor-6' data-look='classic' transform='translate(744.2109375%2c 314)'%3e%3crect class='basic label-container' style='fill:%2300a3cc !important%3bstroke:white !important%3bstroke-width:2px !important' x='-60.6796875' y='-27' width='121.359375' height='54'/%3e%3cg class='label' style='color:white !important' transform='translate(-30.6796875%2c -12)'%3e%3crect/%3e%3cforeignObject width='61.359375' height='24'%3e%3cdiv style='color: rgb(255%2c 255%2c 255) !important%3b display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b' xmlns='http://www.w3.org/1999/xhtml'%3e%3cspan style='color:white !important' class='nodeLabel'%3e%3cp%3ecAdvisor%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='node default exporter' id='mermaid-0-flowchart-PVEExporter-7' data-look='classic' transform='translate(744.2109375%2c 430)'%3e%3crect class='basic label-container' style='fill:%2300a3cc !important%3bstroke:white !important%3bstroke-width:2px !important' x='-78.90625' y='-27' width='157.8125' height='54'/%3e%3cg class='label' style='color:white !important' transform='translate(-48.90625%2c -12)'%3e%3crect/%3e%3cforeignObject width='97.8125' height='24'%3e%3cdiv style='color: rgb(255%2c 255%2c 255) !important%3b display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b' xmlns='http://www.w3.org/1999/xhtml'%3e%3cspan style='color:white !important' class='nodeLabel'%3e%3cp%3ePVE-Exporter%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='node default loki' id='mermaid-0-flowchart-Loki-8' data-look='classic' transform='translate(1012.6171875%2c 639)'%3e%3crect class='basic label-container' style='fill:black !important%3bstroke:white !important%3bstroke-width:2px !important' x='-111.3828125' y='-27' width='222.765625' height='54'/%3e%3cg class='label' style='color:white !important' transform='translate(-81.3828125%2c -12)'%3e%3crect/%3e%3cforeignObject width='162.765625' height='24'%3e%3cdiv style='color: rgb(255%2c 255%2c 255) !important%3b display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b' xmlns='http://www.w3.org/1999/xhtml'%3e%3cspan style='color:white !important' class='nodeLabel'%3e%3cp%3eLoki (Log-Aggregation)%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='node default prometheus' id='mermaid-0-flowchart-Prometheus-9' data-look='classic' transform='translate(432.1875%2c 586)'%3e%3crect class='basic label-container' style='fill:%23E6522C !important%3bstroke:white !important%3bstroke-width:2px !important' x='-130' y='-39' width='260' height='78'/%3e%3cg class='label' style='color:white !important' transform='translate(-100%2c -24)'%3e%3crect/%3e%3cforeignObject width='200' height='48'%3e%3cdiv style='color: rgb(255%2c 255%2c 255) !important%3b display: table%3b white-space: break-spaces%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b width: 200px%3b' xmlns='http://www.w3.org/1999/xhtml'%3e%3cspan style='color:white !important' class='nodeLabel'%3e%3cp%3ePrometheus (Time-Series Metrics)%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3cg class='node default grafana' id='mermaid-0-flowchart-Grafana-10' data-look='classic' transform='translate(117.59375%2c 623)'%3e%3crect class='basic label-container' style='fill:%23F47A20 !important%3bstroke:white !important%3bstroke-width:2px !important' x='-109.59375' y='-27' width='219.1875' height='54'/%3e%3cg class='label' style='color:white !important' transform='translate(-79.59375%2c -12)'%3e%3crect/%3e%3cforeignObject width='159.1875' height='24'%3e%3cdiv style='color: rgb(255%2c 255%2c 255) !important%3b display: table-cell%3b white-space: nowrap%3b line-height: 1.5%3b max-width: 200px%3b text-align: center%3b' xmlns='http://www.w3.org/1999/xhtml'%3e%3cspan style='color:white !important' class='nodeLabel'%3e%3cp%3eGrafana (Dashboards)%3c/p%3e%3c/span%3e%3c/div%3e%3c/foreignObject%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/g%3e%3c/g%3e%3cdefs%3e%3cfilter id='mermaid-0-drop-shadow' height='130%25' width='130%25'%3e%3cfeDropShadow dx='4' dy='4' stdDeviation='0' flood-opacity='0.06' flood-color='black'/%3e%3c/filter%3e%3c/defs%3e%3cdefs%3e%3cfilter id='mermaid-0-drop-shadow-small' height='150%25' width='150%25'%3e%3cfeDropShadow dx='2' dy='2' stdDeviation='0' flood-opacity='0.06' flood-color='black'/%3e%3c/filter%3e%3c/defs%3e%3c/svg%3e)
Under Docker the configuration is mostly a copy-paste job. Only the Proxmox exporter needs manual work, since you have to create an API token with the right permissions in the PVE interface.
Dashboards
At grafana.com/dashboards there’s a large selection of community dashboards you can import by ID. My favorites:
- Node Exporter Full: everything about the host.
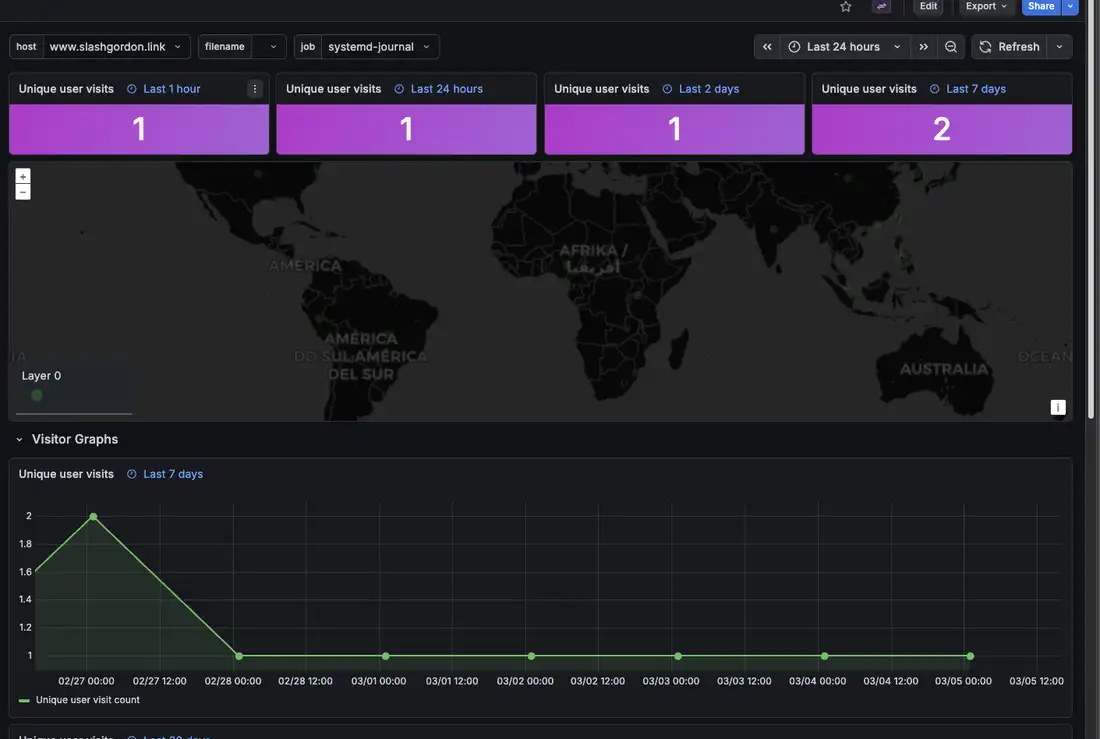
- Nginx Web Analytics: who’s coming from where?
- cAdvisor Exporter: what are my containers eating?
- SSH Logs: who is trying to log in via SSH?
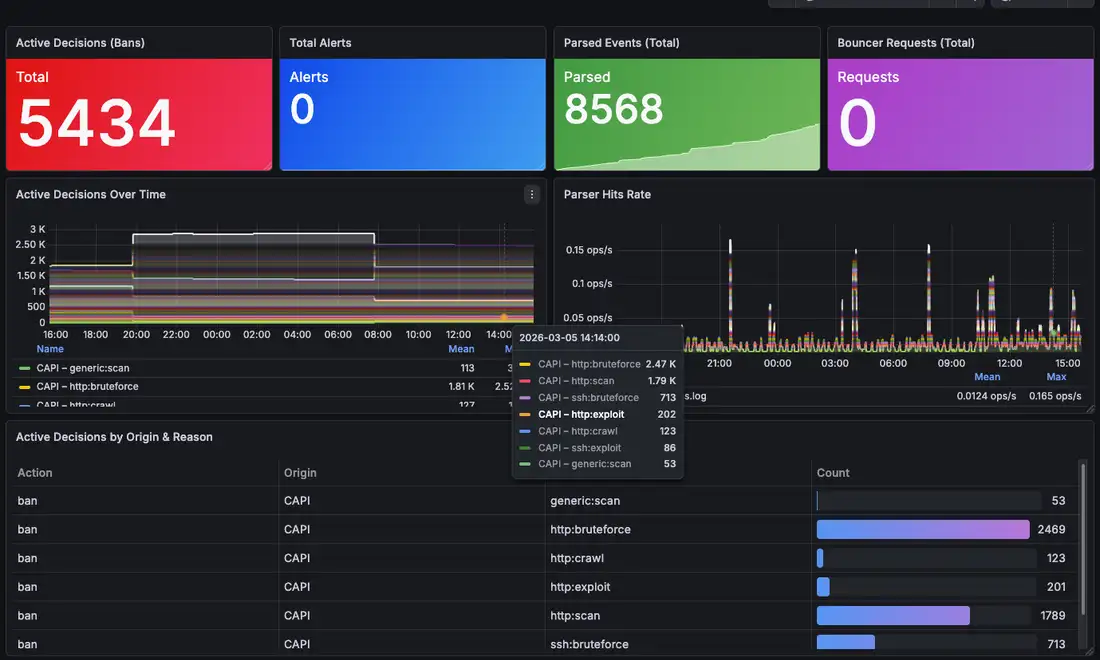
- CrowdSec Metrics: who’s already been kicked out?
Provisioning runs from YAML files, so everything comes back instantly after a fresh install. The details are in my GitHub repo.
First discoveries: hello, botnet
As soon as the first Nginx logs showed up in Grafana, there was a lot more traffic than I expected. A second look showed that most of it came from bots.
I was getting hammered with 404s for paths like /tool.php, /admin-footer.php, or /abc.php. My sites are static HTML built with Astro, so there is nothing here for a PHP exploit to find, but the bots keep trying every second anyway.
Log excerpt (anonymized):
request for /tool.php with HTTP status: 404 from 172.22.0.8 located in ITrequest for /jga.php with HTTP status: 404 from 172.22.0.8 located in IT
The fix: Traefik and CrowdSec
I thought Cloudflare’s free plan would catch all of this. It doesn’t, plenty of these scans still get through. And since Traefik sits behind the Cloudflare proxy, it normally only sees the Cloudflare IP, so a ban would block the proxy itself.
The answer is CrowdSec, the modern successor to fail2ban, plus a Traefik plugin. The label forwardedHeadersCustomName=CF-Connecting-IP tells the CrowdSec plugin to read the real visitor IP from the Cloudflare header.
Here is my docker-compose.yml snippet for the two of them:
version: "3.8"

services:
  crowdsec:
    image: crowdsecurity/crowdsec:latest
    container_name: crowdsec
    restart: unless-stopped
    # Entrypoint handles the bouncer key from secrets
    entrypoint: ["/bin/sh", "-c", "export BOUNCER_KEY_traefik=$(cat /run/secrets/crowdsec_bouncer_key) && exec /docker_start.sh"]
    environment:
      COLLECTIONS: "crowdsecurity/traefik crowdsecurity/http-cve crowdsecurity/base-http-scenarios"
    volumes:
      - crowdsec-config:/etc/crowdsec
      - crowdsec-data:/var/lib/crowdsec/data
      - traefik-access-logs:/var/log/traefik:ro
    networks:
      - apps
      - monitoring_net
    secrets:
      - crowdsec_bouncer_key

  traefik:
    image: traefik:v3.6.6
    container_name: traefik
    restart: unless-stopped
    depends_on:
      - crowdsec
    command:
      - "--accesslog=true"
      - "--accesslog.filepath=/var/log/traefik/access.log"
      - "--experimental.plugins.crowdsec-bouncer.modulename=github.com/maxlerebourg/crowdsec-bouncer-traefik-plugin"
      - "--experimental.plugins.crowdsec-bouncer.version=v1.4.1"
    labels:
      - "traefik.enable=true"
      - "traefik.http.middlewares.crowdsec.plugin.crowdsec-bouncer.crowdseclapihost=crowdsec:8080"
      - "traefik.http.middlewares.crowdsec.plugin.crowdsec-bouncer.forwardedHeadersCustomName=CF-Connecting-IP"
    networks:
      - cloudflare
      - apps
The middleware in action
From here I just add the middleware label to every web service (portfolio, blog, and so on). Every request gets checked against the CrowdSec database, and if an IP is flagged as malicious, Traefik blocks it immediately.
blog-astro-web-prd:
  image: nginx:alpine
  labels:
    - "traefik.enable=true"
    - "traefik.http.routers.blog-astro-prd.rule=Host(`www.slashgordon.link`)"
    - "traefik.http.routers.blog-astro-prd.middlewares=crowdsec@docker"
Is it worth the effort?
For me, yes. It’s reassuring to open Grafana and watch the banned-IPs count climb while the CPU load of my 35-watt roommate stays flat. The dashboard also makes the effect obvious: as soon as a bot starts scanning my .php paths, it’s blocked after a few attempts.